

Security and privacy

The LMS your IT team will happily sign off on

Every customer runs in its own isolated database, backups are encrypted and kept in the European Union, and we sign a GDPR data processing agreement with the EU Standard Contractual Clauses. Access is scoped to the person and their team, and you can run the whole thing under your own brand.
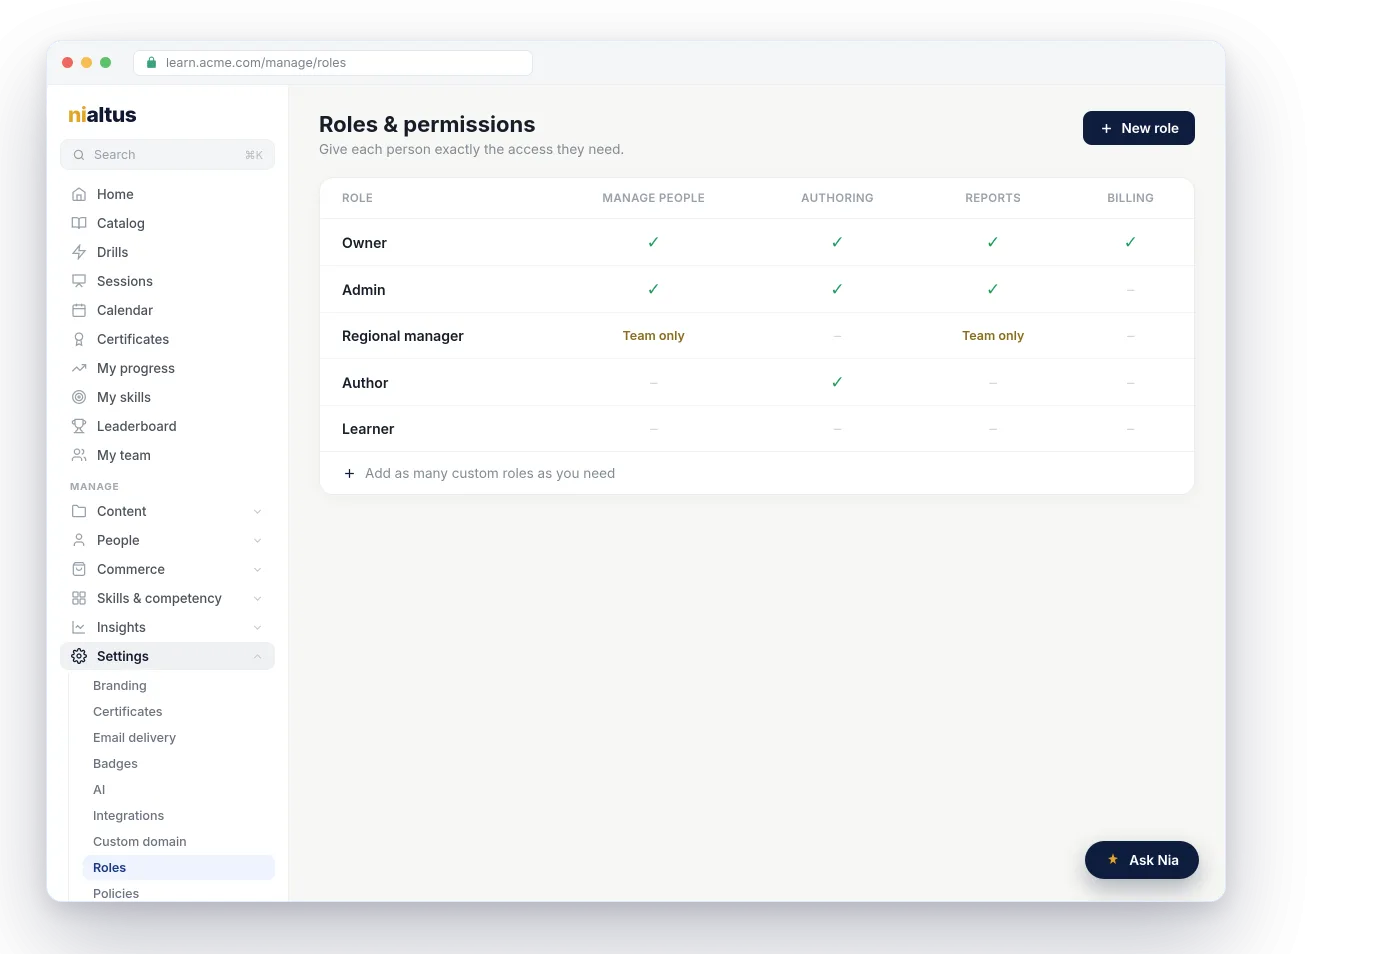
Nialtus roles and access settings
Isolated database per customer
Custom roles and access
Your brand, your domain
Your email, your keys
Privacy and policy controls

Three ways we keep your program safe

Security is not a page in a policy binder. It is how the platform is built, so you can hand it to legal and IT without a long list of caveats.

Your data stays yours

Each customer lives in its own database, not a shared table with everyone else. When you connect email or payments you use your own keys, so your credentials never leave your control. Need to export or remove your data? Just ask, it is yours.

Only the right people get in

Build your own roles and give each one exactly the right permissions (Growth and above). Hand a regional manager a scoped admin view of just their own people, without opening up the whole platform. Access fits your org chart, not the other way around.

Privacy and policies, built in

Publish your privacy policy, terms, and codes of conduct right inside the platform, and have learners accept them before they start. Update a version and your people re-confirm, so your consent trail stays current without a side spreadsheet.

Data protection and hosting

Built for organizations that answer to the GDPR. Where your data lives, how it is protected, and what we commit to in writing. Live service status is always at status.nialtus.com.

Where your data lives

Nialtus runs on servers in India, with all traffic delivered and protected by Cloudflare. For customers in the European Union, the application, databases, files and backups are hosted in the EU, set up before any of your people’s data is loaded.

Encrypted, tested backups

Every workspace is backed up each night and in a full weekly archive. Backups are encrypted before they leave our server and kept in the EU, locked for 30 days so no one can delete or change them. Every month we restore one to prove it works.

A GDPR contract you can sign

You are the controller and we are your processor. We sign a data processing agreement under Article 28 of the GDPR, with the EU Standard Contractual Clauses, a transfer impact assessment and our list of sub-processors.

Told within 48 hours

If an incident affects your data, we tell you without undue delay and within 48 hours, so you can meet your own 72-hour deadline. Your admins can log and track incidents in Nialtus with a 72-hour clock.

Your data, your rules

Export a person’s records or your whole workspace, erase or anonymize people, and set a retention period for dormant accounts. When your contract ends, we delete your workspace within 30 days, after offering you an export.

Straight about certifications

We do not hold ISO 27001 or a SOC 2 report yet, and we will not say we do. We answer your security questionnaire in full and share our security measures in writing.

One customer, one database

Many platforms put every customer’s records in the same shared tables and keep them apart with a filter in the code. Nialtus does not. Your learners, courses and results live in a database of their own, and your uploaded files sit in a folder of their own. It is a cleaner line for your auditors, and it means one customer’s data can never accidentally surface in another’s reports.

  • Records isolated at the database level, not just by a code filter
  • Run on your own domain, under your own brand
  • Bring your own email and payment keys
  • Export or delete your data on request
YOUR ORGANIZATION
Your database
Learners, courses, results, certificates
ANOTHER CUSTOMER
Separate database
Walled off, never in your reports
Data kept apart at the database level

Consent you can actually show

Keep your privacy policy, terms, and codes of conduct in one place and have every learner accept them on their way in. When you publish a new version, people re-confirm, so you always have a clean answer to a simple question: did they agree, and to which version?

  • Publish privacy, terms, and conduct policies
  • Learners accept before they start
  • New version, fresh acceptance
Policies
Learners accept these before they start
Privacy Policyv3Published
Terms of Usev2Published
Code of Conductv1Published
98% of active learners have accepted the current versions

Runs entirely in your brand

Add white-label and run Nialtus entirely as your own. Your logo, your colors, your domain, and mail from your own address, so your learners see your organization from start to finish and never a trace of ours.

  • Your own domain and SSL
  • Your logo, colors, and login screen
  • Notifications from your own email
  • No Nialtus branding anywhere learners look
learn.acme.com
acme academyCourses  Paths  My learning
Welcome back, team
Your training, your brand, your web address.

The controls you expect, built in

The switches and safeguards your admins, IT, and security reviewers ask for, ready on day one.

White-label and custom domains
Your logo, your colors, your web address. Learners never see ours.
Custom roles and permissions
Define your own roles and set exactly what each can see and do.
Delegated admins
Give team and regional leads admin powers scoped to just their people.
Bring your own keys
Connect email and payment providers with your own credentials.
Send from your own email
Deliver notifications over your own SMTP or Microsoft mail.
Privacy and policy controls
Publish versioned policies and collect acceptance from every learner.
Single sign-on and SCIM
SAML 2.0 or OpenID Connect with your identity provider on Growth, Scale, and Enterprise, and SCIM 2.0 provisioning on Scale and Enterprise. See single sign-on.
Two-factor authentication
Anyone can turn on two-factor sign-in with an authenticator app, with one-time recovery codes.
Audit log
A record of sensitive admin actions, such as settings changes, assignments and refused sign-ins, on every plan.

Nialtus is built and run by Learning Everest, a training company that has answered these same security questions for enterprise clients for years. We know what your reviewers will ask, because we have sat on your side of the table.

Questions your security team will ask

Straight answers to the ones we hear most. If yours is not here, ask us on a call and we will walk you through it point by point.

Have a security questionnaire?

Send it over and we will complete it for your account, then walk your IT and security teams through anything that needs a conversation.

Book a security review

Each customer is provisioned with its own database, so your records are held apart from every other customer at the storage level, not merely filtered in code. Uploaded files are kept in object storage under a separate folder for each workspace. Nialtus runs on servers in India (Mumbai), with all traffic delivered and protected by Cloudflare. For customers in the European Union, we host the application, databases, files and backups in the EU, set up before any of your people’s data is loaded. Encrypted off-site backups are already kept in the EU for every customer.
You decide. Access is governed by roles you define, and you can create scoped, delegated admins so a team lead only sees their own people. Build as many custom roles as your structure needs.
Yes, with white-label, which is included on Growth and above and available on Launch as an add-on. You run on your own domain, with your logo and colors, so learners only ever see your brand, not ours.
Yes. You connect email delivery and payment gateways with your own keys, so your credentials stay with you and messages come from your own address.
Publish your privacy policy, terms, and codes of conduct inside the platform and have learners accept them before they start. Publish a new version and your people re-confirm, so your consent record stays current.
Yes. Your data is yours. Your admins can export people’s records and reports at any time, and we provide a full export on request. When your contract ends, we delete your workspace within 30 days, after offering you an export. Encrypted backups that contain it expire on a fixed schedule, within 90 days. We confirm the deletion in writing.
Yes, on Growth, Scale, and Enterprise. Connect Microsoft Entra ID, Okta, Google Workspace, OneLogin, Oracle OCI IAM or any SAML 2.0 or OpenID Connect provider, create accounts at first sign-in, and provision people with SCIM 2.0 on Scale and Enterprise. You can also require single sign-on for everyone except a full administrator with two-factor turned on. See single sign-on and SCIM.
Yes. Any user can turn on two-factor sign-in from their profile with an authenticator app such as Microsoft Authenticator, Google Authenticator or 1Password, and gets one-time recovery codes in case they lose their device.
Yes, on every plan. Sensitive administrative actions are recorded, such as settings changes, training assignments, single sign-on changes, refused sign-ins, two-factor changes and privacy requests. Admins see it under Reports, Audit.
Yes. You are the controller of your workspace data and Nialtus, operated by Learning Everest Private Limited, is your processor. We sign a data processing agreement under Article 28 of the GDPR. For customers in the EU it includes the EU Standard Contractual Clauses for our team’s access from India, and we provide a transfer impact assessment and our list of sub-processors. Email [email protected] to request them.
All traffic is encrypted in transit, and our servers only accept connections that come through Cloudflare. Every workspace database is backed up each night, and a full encrypted archive is made every week. Backups are encrypted on our server before they leave it, then stored off-site in the European Union in a bucket that is locked for 30 days, so no one can delete or change them during that time. Every month we restore a backup on a separate server to prove it works.
If an incident affects your data, we tell you without undue delay and within 48 hours of becoming aware of it, so you can meet your own 72-hour GDPR deadline. Your admins can also log and track incidents inside Nialtus, with a 72-hour clock on each one.
Not yet, and we will not say we are. We will answer your security questionnaire in full, share our data processing agreement and security measures, and walk your team through anything that needs a conversation.
Email [email protected] with “Security” in the subject line. We reply within one working day and keep you updated until the issue is resolved.

Bring your toughest security questions

Book a 20-minute call. Bring your IT lead or your checklist, and we will go through it point by point in your own brand.